Security telemetry & identity
Connecting firewall visibility, network context and identity-based access control.
- My role
- Solution designer & implementation collaborator
- Context
- Enterprise security · Integrated operations
- Project status
- Designed & implemented with the team
Delivered workstreams
- Unifiedfirewall event analysis
- Integratednetwork access control
Splunk integration, event correlation and Cisco ISE implementation with the team. The exact firewall and authentication matrix is not confirmed.
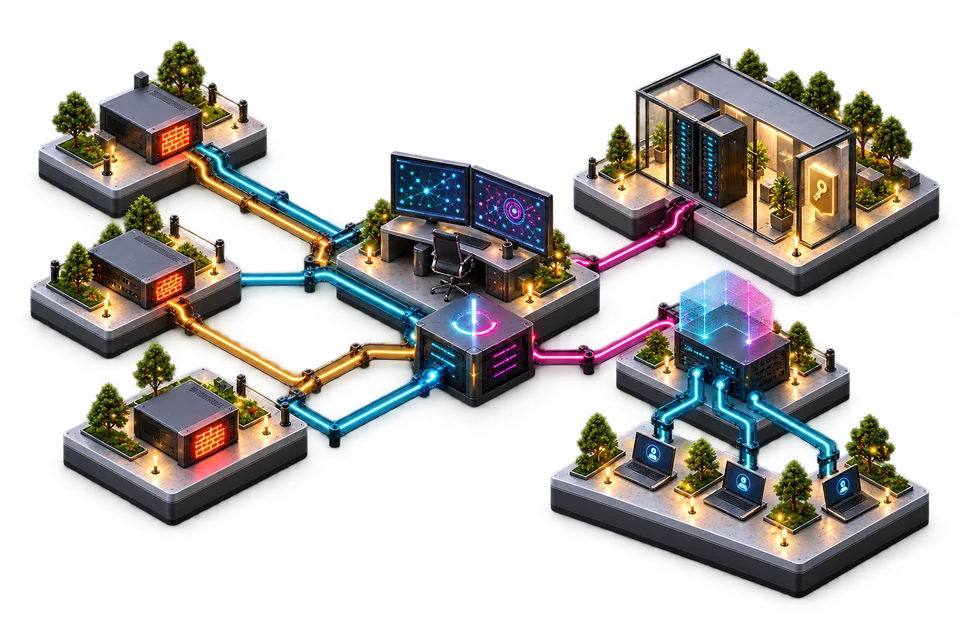
Inside the work
How I approached it
Collect & correlate
Integrate firewall information into Splunk and correlate events with Catalyst Center.
Design NAC
Design and implement Cisco ISE with the delivery team.
Connect identity
Bring authentication, directory and certificate dependencies into the access architecture.
Document & enable
Make the relationships between telemetry, identity and network access understandable for the operating team.
Decisions & trade-offs
Architectural reasoning based on the supplied project account.
Add context to telemetrySplunk plus Catalyst Center correlation
Splunk plus Catalyst Center correlation
Firewall events become more useful for investigation when interpreted alongside network context.
The trade-off
Correlation requires consistent source data and careful interpretation; an event alone is not a diagnosis.
Design the identity dependenciesCisco ISE and NAC
Cisco ISE and NAC
Network access control depends on the relationship between identity services, authentication and policy enforcement.
The trade-off
Certificates, directory services and authentication paths are operational dependencies, not optional details.
Technologies by purpose
Confirmed project technologies
 Splunk
 Cisco ISE
- Catalyst Center
- Firewall event integration
Broader security competencies
Experience relevant to this domain; these products and methods are not all confirmed as deployed in this engagement.
 Palo Alto Networks
 Fortinet
 Check Point
- 802.1X
- RADIUS
- TACACS+
- PKI
- Certificate authorities
- Domain controllers
Scope & evidence
About this case
Owner project account, October 22, 2026. Two workstreams within the described security engagement, not two invented clients.
Carlos on LinkedInProject account
The account describes Splunk integration, event correlation and Cisco ISE design and implementation with the team. Specific firewall products and identity methods are shown as competency context; the exact project matrix remains to be confirmed. No incident-reduction metric is asserted.
Owner-reported account. Private client configurations and original architecture documents are not published with this case.