Automated microsegmentation
Automating provisioning and microsegmentation across a mixed microservices environment.
- My role
- Automation architect & implementation lead
- Context
- Costa Rica · Hybrid infrastructure
- Project status
- Designed & implemented
Implemented scope
- Automatedprovisioning mechanisms
- Integratedsegmentation workflow
Automation mechanisms designed and implemented by Carlos. No quantified security or deployment-time result was supplied.
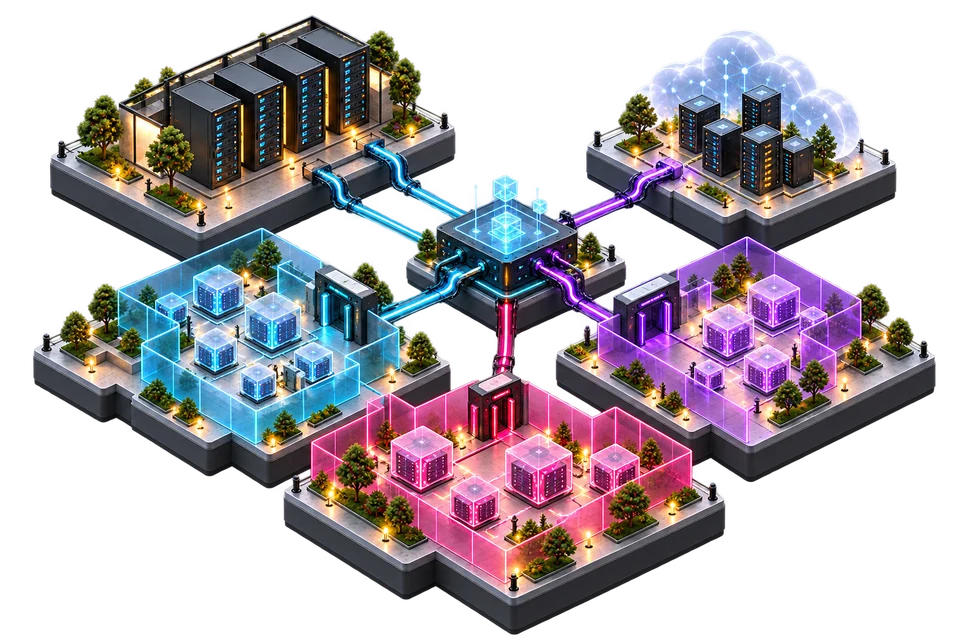
Inside the work
How I approached it
Understand the boundaries
Map the platform mix and the provisioning responsibilities.
Model in Terraform
Design the automation mechanisms for building and provisioning the environment.
Integrate policy
Include microsegmentation in the provisioning workflow.
Implement
Build and implement the automation mechanisms as part of the solution.
Decisions & trade-offs
Architectural reasoning based on the supplied project account.
Treat provisioning as a modelTerraform-based automation
Terraform-based automation
Terraform was selected to define the provisioning mechanisms instead of relying on repeated local manual processes.
The trade-off
The automation model must represent dependencies and platform differences clearly.
Respect platform differencesKubernetes, OpenShift and IBM Power LPARs
Kubernetes, OpenShift and IBM Power LPARs
Microservices and infrastructure boundaries had to coexist across a heterogeneous hybrid environment.
The trade-off
A consistent provisioning intent does not mean every platform exposes identical controls.
Technologies by purpose
Provisioning & microservices
 Terraform
 Kubernetes
 OpenShift
- Microsegmentation
Hybrid platform context
- IBM Power
- LPARs
- Hybrid cloud
Scope & evidence
About this case
Owner project account, October 22, 2026. Client identity and private configurations withheld.
Carlos on LinkedInProject account
Carlos designed and implemented the automation mechanisms. Quantified deployment-time and security-impact results have not been supplied.
Owner-reported account. Private client configurations and original architecture documents are not published with this case.